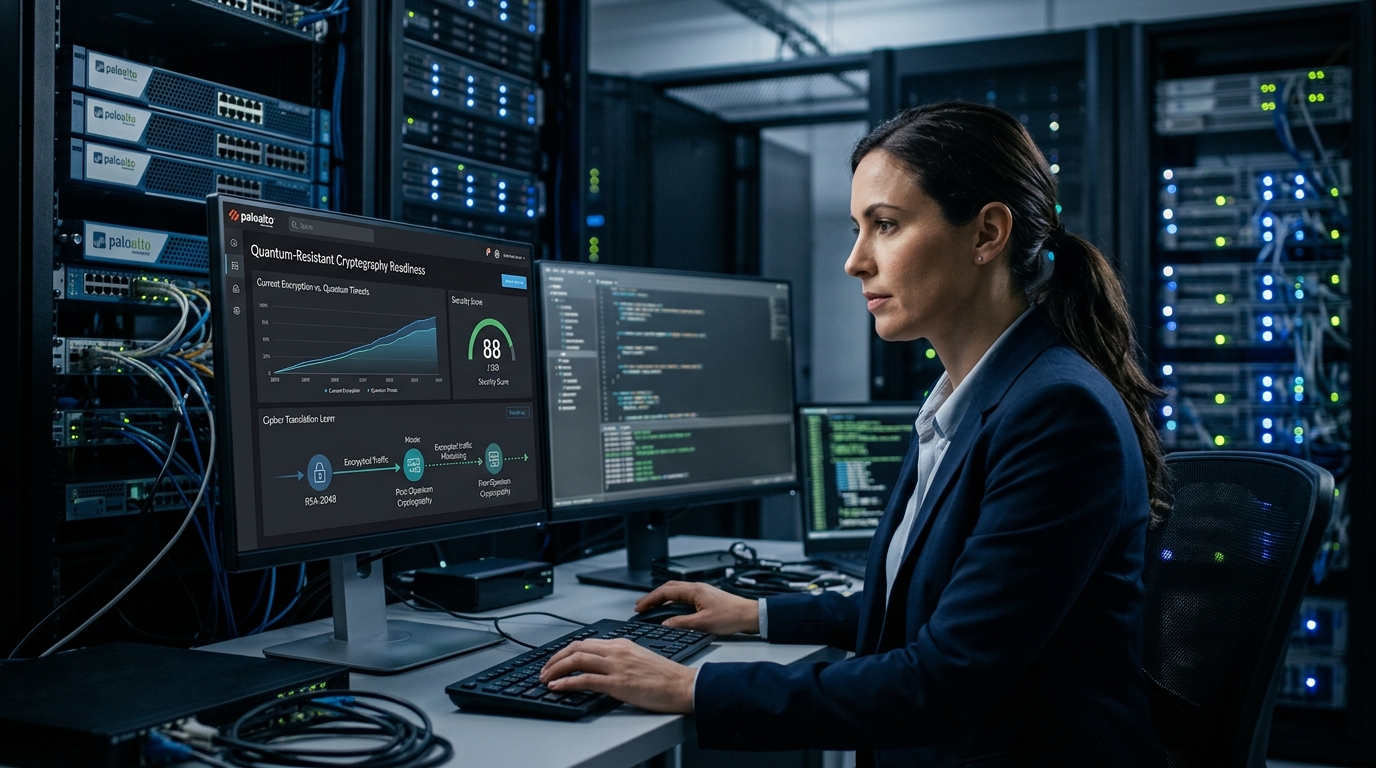
The clock that matters most in enterprise cybersecurity right now is not measured in quarters. It is measured in qubits. And Palo Alto Networks is betting its platform strategy on getting there first.
Why the urgency is real. Three academic papers published between May 2025 and March 2026 cut the estimated physical-qubit count needed to break RSA-2048 from roughly 20 million to potentially fewer than 100,000, prompting Google and others to point their post-quantum migration timelines toward 2029-2030. That compression is not theoretical risk management; it is the operating assumption PANW is building product around. Rich Campagna, a senior vice president at Palo Alto Networks, has said the company is operating on an assumption that Q-Day is within roughly three to four years.
The gap between awareness and action inside enterprises is the market PANW is targeting. DigiCert’s 2026 Quantum Readiness Outlook found that 85% of IT and security leaders believe quantum computing will break today’s encryption standards within a decade, yet only 7% say they have deployed quantum-safe or hybrid certificates on a meaningful scale. The Thales 2026 Data Threat Report: Quantum & AI Trends names harvest-now, decrypt-later the top quantum concern, cited by 61% of respondents. The attack vector is simple: adversaries capture encrypted traffic today and stockpile it until a capable quantum machine arrives to decrypt it retroactively.
The product angle the market is under-pricing. Rather than requiring enterprises to rip and replace legacy infrastructure, PANW’s Cipher Translation Proxy intercepts traffic secured with classical encryption and re-encrypts it in real time using quantum-safe algorithms such as ML-KEM at the network edge, moving legacy assets to a quantum-safe posture without backend code changes. Palo Alto Networks has also positioned its Quantum-Optimized Hardware portfolio around higher-performance processing of post-quantum cryptography, including a set of 14 new 5th-generation next-generation firewall models it introduced alongside its cipher translation launch. For the installed base of global enterprise customers, this is a renewal and upsell catalyst, not a one-time hardware event.
The carrier channel amplifies that reach. AT&T and Palo Alto Networks publicly described a quantum-resilient SASE fabric collaboration in July 2026, combining cryptographic capabilities from Palo Alto’s Prisma SD-WAN with AT&T’s global network. The combined architecture is designed to safeguard distributed enterprise perimeters against harvest-now, decrypt-later threats without introducing network latency or requiring complete hardware replacement at remote branch locations.
The AT&T partnership adds a carrier-scale distribution layer, but AT&T’s own financial footing shapes how aggressively it can co-invest. AT&T’s free cash flow trajectory determines how much capital it can commit to joint infrastructure buildouts like this one.
The numbers behind the thesis. Full fiscal year 2026 revenue reached $11.5 billion, up 24% year over year. Next-Generation Security ARR grew 63% to $9.10 billion, while remaining performance obligations climbed 34% to $21.2 billion. That RPO figure is the one traders should map against the quantum rollout: contracted future revenue gives PANW time to convert quantum readiness from a marketing feature into a measurable renewal driver. As of mid-October 2026, aggregated Wall Street consensus data commonly shows roughly 55 analysts at a Buy-equivalent consensus, with an average 12-month price target around $398.
Technical levels to watch. PANW sat at $375.04 on October 14, with RSI at 45.9, support at $363.58, and resistance at $419.91. The price is below the 20-day moving average at $392.28 but just above the 50-day at $373.46, a mixed picture rather than a confirmed trend break. A hold of the $363-$373 support band keeps the structure constructive. A close below $363 shifts the focus to the three-month low near $308.
The compliance pressure tightening underneath the trade: September 21, 2026 marked the NIST CMVP transition date after which FIPS 140-2 validations move off the active list and into Historical status. That transition is widely treated across federal-facing security programs as a forcing function toward FIPS 140-3 validated implementations for future procurement and refresh cycles. Every enterprise bidding on federal contracts now has a technical requirement, not just a strategic preference. That is the catalyst embedded in PANW’s pipeline that consensus models are still treating as background noise.